Executive summary
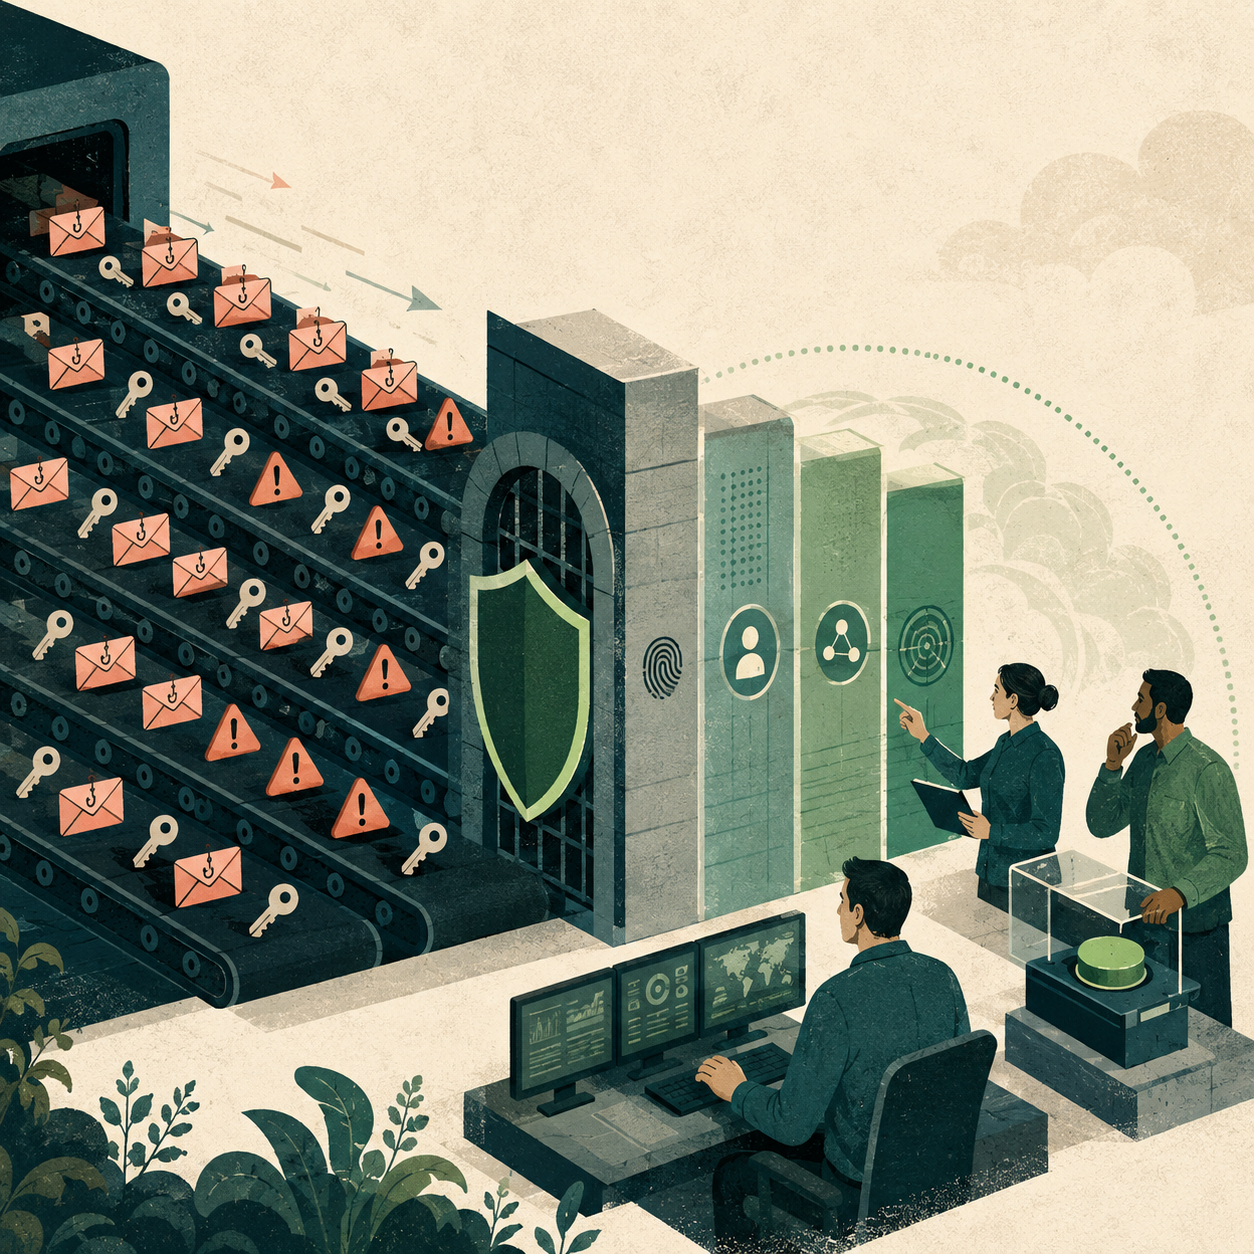
Decision briefThere is no trustworthy global count of breaches caused solely by AI. The stronger evidence is that attackers increasingly use AI to accelerate familiar work: research, phishing, exploit development, malware modification, impersonation, and automation.
- IBM finding
- AI-driven attacks increased 56% in IBM's 2026 research.
- Average impact
- IBM reports a record $4.99 million global average breach cost.
- Business response
- Faster attacks make identity, patching, monitoring, backup, and response speed more important.
A realistic example
An attacker once spent days researching employees, suppliers, software, and writing style before attempting a targeted intrusion. AI can compress parts of that preparation into hours by organizing public information, producing localized messages, troubleshooting code, and repeating variations. The attack still depends on a real opening such as a stolen credential, vulnerable system, excessive permission, or successful deception.
Before and after
Before
- AI-enabled attacks are dismissed as theoretical or limited to elite attackers.
- Annual awareness training is treated as the primary phishing defense.
- Patches, account reviews, and incident exercises move on slow schedules.
- Unapproved AI tools and agent connections grow without a reliable inventory.
After a controlled improvement
- AI is treated as an accelerator across the existing attack lifecycle.
- Phishing-resistant identity controls reduce dependence on recognition alone.
- Critical vulnerabilities, exposed credentials, and unusual access receive rapid response.
- AI systems, data access, agent identities, connectors, permissions, and audit history are governed together.
Six priorities for machine-speed pressure
Strengthen identity
Use phishing-resistant multifactor authentication where practical, remove dormant accounts, restrict privileges, and independently verify sensitive requests.
Reduce the patch window
Maintain an accurate asset inventory, prioritize internet-facing and exploited vulnerabilities, and verify remediation.
Control AI access
Inventory approved models, agents, data sources, connectors, service accounts, and permissions. Block unnecessary external access and shadow AI use.
Monitor useful signals
Watch for unusual authentication, access, data movement, agent behavior, and configuration changes instead of relying on one AI security product.
Protect recovery
Keep tested, isolated backups and document how essential operations continue when identity, network, or AI services are unavailable.
Practice response
Exercise impersonation, credential compromise, data exposure, ransomware, and an AI agent acting outside its approved boundary.
Tools and process components
- Phishing-resistant multifactor authentication and conditional access
- Asset, vulnerability, and patch-status inventory
- Endpoint, identity, network, and data-access monitoring
- Email authentication and out-of-band verification procedures
- AI system, model, agent, connector, and permission inventory
- Isolated backups and practiced incident-response playbooks
Safeguards to keep
- Do not claim every modern breach is AI-driven; attribution and technology use are often incomplete.
- Do not treat AI security products as substitutes for identity, patching, minimum permissions, monitoring, backup, and response fundamentals.
- Do not permit AI agents to inherit broad user or administrator access without scoped identities, runtime controls, and auditability.
- Do not publish sensitive incident details, credentials, indicators, or customer data while discussing AI-enabled threats.
Source and update policy
Verify product details before you build.
Vendor capabilities, plan limits, security guidance, and terms change. CSLM reviewed the following references for this guide. Confirm current first-party documentation and obtain qualified advice when required before selecting or configuring a service.
Continue the topic
Related practical guides
The practical takeaway
AI may accelerate the attack. Fundamentals still decide whether it becomes a breach.